Office of National Security Reviews Comprehensive Survey of Civilian, Government and Military IT Assets
Cross-check System and Network Diagrams Against Actual Assets
Seek to Obtain Vulnerability Information Before Public Disclosure
Accelerate Adoption of Software Bills of Materials (SBOMs)
The National Security Office reviewed the progress of a comprehensive survey of information technology (IT) assets across the private, public, and defense sectors, which has been underway since August. The survey aims to address delays in responding to newly discovered vulnerabilities caused by discrepancies between the systems and network diagrams held by institutions and the assets they actually operate. The office will develop measures to obtain and share vulnerability information before it is publicly disclosed and accelerate the adoption of Software Bills of Materials (SBOMs).

The phoenix flag flies at Cheong Wa Dae in Seoul on Dec. 29, 2025, as President Lee Jae-myung heads to work there, officially ushering in the return of the Cheong Wa Dae era after three years and seven months. Photo by Jo Yongjun
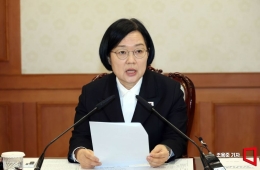
View original imageThe National Security Office said on Nov. 15 that it had conducted an interim review of the comprehensive survey of systems and network diagrams at a joint public-private-military cybersecurity response meeting held on Nov. 13 and chaired by Song Ki-ho, the office's Third Deputy Director. The meeting also included a joint assessment of major cyber incidents in South Korea and abroad.
The office explained, "As cyberattacks using artificial intelligence (AI) increase, discrepancies between the systems and network diagrams of some institutions and their actual assets have made it difficult to take swift action when new vulnerabilities are identified."
Accordingly, since August, the office has been working with the Ministry of Science and ICT, the National Intelligence Service, and the Ministry of National Defense, which are responsible for responding to cyber crises in their respective sectors, to establish a management system that provides a comprehensive inventory of information assets, including hardware and software. The office plans to establish the system as soon as possible so that actual operating conditions are reflected in the diagrams.
Hot Picks Today
 "Two Spend 500,000 Won in a Flash, Yet Wait Two Hours?" ... 'Dreamland' Shunned by Kids and Foreign Tourists
- The Era of Getting 200 Million Won After 30 Years Is Over... A Japanese Bank's "Perpetual Department Head" Who Just Clocked In Cries Out
- Spain Hit by Its Worst Tragedy... Lee Kangin, Moreno and Real Madrid Join Soccer World in Mourning
- They Said, “Make It Your Home for Life” - Then Suddenly Kicked 200 Passengers Off... What Happened to the Around-the-World Cruise?
- "130 Rice Bowls Sold Out in a Day"... 'Unfiltered Face' Adds 8 Million Won to Night Market Sales: China's Bungeunwoo
The office will also develop measures to obtain vulnerability information before it is publicly disclosed through foreign government agencies, software suppliers, and relevant communities, and to share it promptly so preventive measures can be taken. It will accelerate the adoption of documents that record the components used in software so that, when a vulnerability is found in a particular component, affected systems can be identified quickly.
© The Asia Business Daily. All rights reserved. Unauthorized AI training and use prohibited.