Financial regulators to conduct comprehensive security reviews at around 580 companies... Lee Eog-weon: "CEOs will be held accountable for poor security management" (Comprehensive)
Comprehensive review of external-facing points and internal control systems, including those overseen by CEOs
Vulnerability assessments at large financial companies to increase from once to twice a year
TF to fully lift network-separation regulation
The Financial Services Commission (FSC) will conduct a comprehensive review of the external-facing security of all IT assets and the operation of internal control systems, including those overseen by chief executive officers (CEOs), at approximately 580 companies across the financial sector. It will also launch a task force (TF) to fully lift network separation regulations and build a new AI-based security framework. The measures aim to overhaul security across the financial sector following a succession of hacking incidents involving banks, insurers, virtual asset businesses, electronic financial businesses and online investment-linked financial businesses. The FSC plans to hold financial companies’ executives, including CEOs, strictly accountable for leaving security vulnerabilities unaddressed or failing to respond adequately to incidents.
Lee Eog-weon: "CEOs Will Be Held Accountable for Poor Security Management"

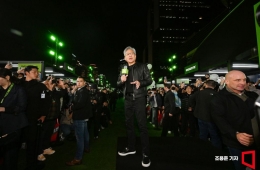
Lee Eog-weon, chairman of the Financial Services Commission, speaks at a meeting with representatives from across the financial sector on innovating security systems in the AI era, held at the Financial Security Institute in Yeouido, Seoul, on November 5, 2026. Photo by Kim Hyun-min
View original imageOn the 5th, the FSC announced these measures at a meeting titled "All-Financial-Sector Meeting to Innovate Security Systems in the AI Era," chaired by Financial Services Commission Chairman Lee Eog-weon and attended by heads of financial sector associations, the Financial Supervisory Service and the Financial Security Institute, among others.
Chairman Lee said, "Security is not a technical issue for a particular department; it is a core management responsibility for which the CEO must be directly accountable." He added, "We will hold executives, including CEOs, strictly accountable under relevant laws and regulations for serious management failures or inadequate responses." He also urged them to act, saying, "A financial company that cannot protect its customers' information and assets has already lost its reason to exist. CEOs across the financial sector should immediately form company-wide emergency response teams and work to establish robust security systems."
This means that responsibility for the successive hacking incidents in the financial sector will be treated not as an issue for IT departments alone, but as an internal control matter that CEOs must directly manage and oversee. Last month, Financial Supervisory Service Governor Lee Chan-jin also said at a parliamentary audit, "With regard to the duty to manage internal control standards, cybersecurity and this hacking incident will be the first case in which the issue of CEO accountability is addressed." The heads of the financial authorities have thus stressed executives' responsibility in succession, making clear that CEOs must personally oversee security management and incident prevention.
According to the FSC, 40 cyber incidents were reported by 37 financial companies after September 30. The scale of information exposure was estimated at approximately 473,000 records. At some small virtual asset exchanges, electronic financial businesses and online investment-linked financial businesses, company-managed funds were stolen, with reported losses totaling approximately 1 billion won.
Comprehensive Security Review of Around 580 Financial Companies...Vulnerability Assessments to Increase to Twice a Year

The FSC will conduct a comprehensive review at approximately 580 companies, including banks, insurers, securities firms, electronic financial business operators, online investment-linked financial business operators and virtual asset service providers. The review will cover all external-facing IT assets, including APIs, as well as the operation of internal control systems. It will include not only customer-facing services such as websites, but also all business areas accessible from outside, including employee management, internal operations and partner-related operations.
The review will also examine internal control systems, including the roles and responsibilities of CEOs, chief information security officers (CISOs) and chief information officers (CIOs); decision-making procedures for creating, operating and decommissioning external access points; and whether IT asset inventories are maintained. If serious vulnerabilities are found, the FSC plans to require services to be suspended immediately and external access to be blocked. The FSC will complete the comprehensive security review by the end of the year and use its findings to prepare and implement "Security Internal Control Guidelines" in the first quarter of next year.
The system for analyzing and assessing security vulnerabilities will also be strengthened. Starting with large financial companies, the frequency of security vulnerability analysis and assessments will increase from once to twice a year, and assessments will be required to cover all external access points directly or indirectly related to electronic financial transactions. The FSC will also establish a legal basis for financial authorities to demand emergency inspections. Measures are being pursued to issue corrective orders when serious vulnerabilities are left unaddressed for an extended period and to impose recurring enforcement fines if those orders are not followed.
Starting in December, the Financial Security Institute plans to provide smaller financial companies with limited security expertise and budgets with its "One-Stop AI Defense Service" on a phased basis. The service uses AI to continuously scan external access points and vulnerabilities and provide response measures.
Fully Lift Network Separation Restrictions...Build a New AI-Based Security Framework
In particular, under the principle that "AI attacks should be stopped with AI," the FSC will launch a TF this month to fully lift network separation regulations. The initiative aims to move away from the existing security framework centered on network separation and build a new AI-based security framework. The government, relevant institutions, the financial sector and private-sector experts will discuss alternative security measures, including data management and protection frameworks tailored to data sensitivity and zero trust, which continuously verifies all access.
The FSC will also make permanent the easing of network separation regulations to enable the use of AI and software as a service (SaaS) for security purposes. In addition to generative AI and business SaaS, it plans to expand exemptions from network separation regulations through the Innovative Financial Services review process to cover a range of IT services, including blockchain.
In addition, the FSC will prepare a "Digital Financial Safety Act" by the first quarter of next year to expand the scope of security regulations. The key measure is to apply security regulations on par with those under the Electronic Financial Transactions Act to sectors that hold large volumes of customer information or where a cyber incident could cause customers direct asset losses, including virtual asset service providers and general agencies (GAs). The FSC will also consider a regulatory framework for third parties, such as cloud and platform providers, that serve multiple financial companies.
Other measures include upgrading the financial sector's joint hacking monitoring system, strengthening surveillance of the illegal sale of personal information on the dark web and improving AI-based voice phishing detection. The FSC will also pursue legislation establishing no-fault liability, under which financial companies would compensate victims for a portion of their losses from voice phishing.
Hot Picks Today
 "Two Spend 500,000 Won in a Flash, Yet Wait Two Hours?" ... 'Dreamland' Shunned by Kids and Foreign Tourists
- The Era of Getting 200 Million Won After 30 Years Is Over... A Japanese Bank's "Perpetual Department Head" Who Just Clocked In Cries Out
- Spain Hit by Its Worst Tragedy... Lee Kangin, Moreno and Real Madrid Join Soccer World in Mourning
- They Said, “Make It Your Home for Life” - Then Suddenly Kicked 200 Passengers Off... What Happened to the Around-the-World Cruise?
- "130 Rice Bowls Sold Out in a Day"... 'Unfiltered Face' Adds 8 Million Won to Night Market Sales: China's Bungeunwoo
Chairman Lee stressed, "The recent succession of cyber incidents in the financial sector is a grave warning that we must fundamentally transform security across our financial system." He added, "The time has come to move beyond existing security management methods and practices and overhaul our security systems across the board."
© The Asia Business Daily. All rights reserved. Unauthorized AI training and use prohibited.