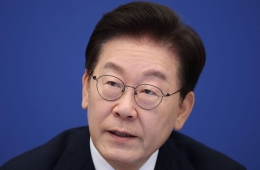
Lee Chanjin: "I Will Hold CEOs of Hacked Financial Firms Strictly Accountable"
Strengthen accountability of executives at large financial firms
Apply the same inspection and sanctions policy as for the banking sector
- Conduct comprehensive inspections of external-facing points, followed by verification of compliance
Lee Chan-jin, Governor of the Financial Supervisory Service (FSS), stressed that the agency would hold the management of large financial companies hit by hacking incidents, including their chief executive officers (CEOs), strictly accountable. He warned that the FSS would conduct a comprehensive inspection of external-facing points across the entire financial sector to prevent further incidents and take stern action if the inspections were merely formalities.

At an executive meeting of the FSS on November 3, Governor Lee reviewed how each sector had responded to recent hacking incidents in the financial industry and discussed measures to strengthen IT security.
Governor Lee stressed that financial companies must establish an autonomous security system that enables them to proactively identify and address security threats and vulnerabilities. "CEOs, other executives and boards of directors must clearly recognize that ensuring IT security is the foundation of customer trust and a core survival strategy, and take the lead in expanding security budgets and staffing next year," he said.
He said the FSS would hold the management of companies affected by incidents accountable to ensure that security is strengthened in a substantive manner commensurate with cyber threats. "For large financial companies, including comprehensive financial investment business entities and insurers, we will hold executives, including CEOs, strictly accountable, in line with the inspection and sanctions policy for the banking sector that we announced earlier," Governor Lee said.
He also said the FSS would work closely with the National Assembly to ensure the swift passage of amendments to the Electronic Financial Transactions Act. The government is currently pursuing amendments that would allow punitive surcharges of 3% of revenue to be imposed without exception when hacking incidents occur due to inadequate basic controls or neglected security vulnerabilities. "Even before the law is amended, we will explore various ways to encourage financial companies to strengthen security, including imposing supervisory levies at different rates depending on factors such as whether an incident has occurred, in accordance with the beneficiary-pays principle," he said.
The FSS will also inspect external-facing points across the entire financial sector. To prevent further incidents, it will require a comprehensive inspection of external-facing points at general agencies (GAs), moneylenders, virtual asset businesses and online investment-linked financing businesses, among others. To ensure the inspections are effective, FSS IT specialists will be fully mobilized to verify afterward whether they were carried out. The FSS plans to take stern action if inspections are merely formalities.
"In particular, external-facing points connected to systems that handle customers' or financial companies' assets, and where an attack could result in financial losses, should be inspected first. In principle, external access should be blocked until vulnerabilities are resolved," he said.
Hot Picks Today
 "Two Spend 500,000 Won in a Flash, Yet Wait Two Hours?" ... 'Dreamland' Shunned by Kids and Foreign Tourists
- The Era of Getting 200 Million Won After 30 Years Is Over... A Japanese Bank's "Perpetual Department Head" Who Just Clocked In Cries Out
- Spain Hit by Its Worst Tragedy... Lee Kangin, Moreno and Real Madrid Join Soccer World in Mourning
- They Said, “Make It Your Home for Life” - Then Suddenly Kicked 200 Passengers Off... What Happened to the Around-the-World Cruise?
- "130 Rice Bowls Sold Out in a Day"... 'Unfiltered Face' Adds 8 Million Won to Night Market Sales: China's Bungeunwoo
He also said the FSS would pursue measures including establishing a dedicated security unit and increasing IT staffing to ensure that supervision and inspections effectively strengthen IT security across the financial sector.
© The Asia Business Daily. All rights reserved. Unauthorized AI training and use prohibited.