[Exclusive] Regular Security Checks Missed Hacking Targets... Authorities Let Financial Firms ‘Self-Select,’ Scrambling for Solutions After Incidents
[Financial Security Loopholes]②
Annual Inspections Left to Banks' Own Discretion
External Endpoints Targeted by Hackers Remain "Blind Spots" in Regular Checks
Authorities Missed Overlooked Assets Despite Reports
Scope of Inspec
As a series of major commercial banks and other financial firms have recently fallen victim to hacking attacks utilizing artificial intelligence (AI), it has come to light that most of the targeted external IT interfaces and other assets were not included in the regular security inspection scope of financial institutions. While financial authorities have mandated annual vulnerability assessments, a loophole in the system has been exposed as the selection of inspection targets has been left up to the "self-selection" of each financial firm. Only after these security incidents did the authorities recognize this oversight, prompting belated moves to improve the system by broadly including external interfaces and other IT assets previously omitted from regular inspections.

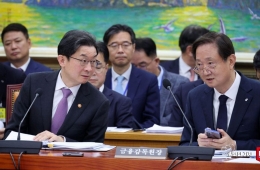
Lee Eokwon, Chairman of the Financial Services Commission (left), and Lee Chanjin, Governor of the Financial Supervisory Service, are attending and conversing at the full meeting of the Political Affairs Committee held at the National Assembly last February. 2026.2.5 Photo by Hyunmin Kim
View original imageAccording to The Asia Business Daily’s coverage on October 6, financial authorities have found that many of the external interfaces targeted in recent hacking attacks on the financial sector were excluded from the vulnerability analysis and assessment regularly conducted by financial companies.
Since September 27, incidents of breaches and information leaks have been confirmed at KB Kookmin Bank, Shinhan Bank, Hana Bank, BNK Busan Bank, as well as at savings banks like Yegaram and Welcome, and modern credit institutions such as Hyundai Capital. The number of incidents ranged from dozens of cases at some firms to as many as 40,000 at others. The attacks focused on external interfaces that are used by loan brokers or employees—systems generally managed with less rigor than the core transaction-processing networks.
An official from a financial regulatory authority stated, "Currently, each financial firm independently determines the scope of assets for security vulnerability assessments.” The official added, “With this incident as a turning point, we have recognized the structural flaw in this arrangement and are now reviewing concrete regulatory improvements, including amendments to the Electronic Financial Supervision Regulation."
Under the current Electronic Financial Transactions Act, financial firms are required to conduct vulnerability analyses and assessments of their "electronic financial infrastructure" and report the results to the Financial Services Commission. According to related ordinances, financial firms with total assets of at least 2 trillion won or regular staff numbers of 300 or more are required to conduct at least one such assessment per year.
The main problem is that not all IT assets owned by a financial institution are automatically included in the assessment target. While the regulation defines the electronic financial infrastructure as "information processing systems and telecommunications networks used in electronic financial transactions," it does not specify exactly which IT assets must be included. Therefore, financial firms have been identifying IT assets on their own and then deciding which qualify as infrastructure, accordingly setting the inspection scope themselves.
This hacking incident exploited precisely this institutional blind spot. IT assets with lower security priority—such as external interfaces or systems independently built and managed by business departments—were left out of regular assessments, making these "weak links" prime targets and exposing gaps in the system. Hackers specifically targeted the “demilitarized zone (DMZ)” that interfaces with external networks, rather than core financial transaction systems. Representative cases include Shinhan Bank’s loan broker inquiry service, KB Kookmin Bank’s staff mobile support system, and Hana Bank’s business support platform. Similarly, last month’s Toss Payments breach also initially targeted an external interface linked to affiliate merchants, showing a comparable attack pattern.

A financial sector official commented, “Business divisions sometimes operate systems independently, and in such cases, even the security department may be unaware of the existence or operational status of those assets. Since including all IT assets in the vulnerability analysis and assessment would require significant costs and manpower, firms have tended to focus on assets they already manage, leaving less-noticed assets out of scope.”
The oversight by financial regulators has also come under scrutiny. While the authorities left the determination of assessment scope to the firms, they failed to effectively filter or confirm whether the coverage was adequate. After completing vulnerability analyses and assessments, financial firms report the reasons, assets, periods, results, and remediation plans to the authorities. The Financial Supervisory Service reviews these submissions and forwards them to the Financial Services Commission, which can require improvements or additional measures if necessary. However, since supervision is based on the self-designated assets of financial firms, any IT assets omitted at the selection stage also escaped the regulators' oversight.
In response to these incidents, financial authorities now plan to include IT assets such as external interfaces—previously in a management blind spot—in regular assessments. They also intend to revise the criteria for target selection, which has so far relied heavily on the firms’ own judgment. Additional measures under review include shortening the current annual assessment cycle and introducing mandatory fines to enhance the effectiveness of required remedial actions.
A regulatory official highlighted, “Financial firms own a vast and growing pool of IT assets, especially with the rapid expansion of non-face-to-face financial services. There is a need for stricter and more comprehensive management of all IT assets, and we plan to establish relevant countermeasures as soon as possible.”
It has also been pointed out that, despite the recent relaxation of network separation rules for financial firms, vulnerability assessments using AI have not become as active as expected.
As AI-driven security threats have grown, the financial authorities relaxed network separation rules—under the principle that “AI should be used to counter AI”—so that financial companies could leverage generative AI for security purposes. Ten companies were exempted on a trial basis from June, allowing them to adopt these measures temporarily. Regulators required these firms to conduct vulnerability assessments using AI and report any identified security risks. However, as the use of AI in security assessments has not been as robust as anticipated, the Financial Supervisory Service recently requested that each financial firm submit details on its use of AI, target services, utilized programs, and discovered vulnerabilities.
Hot Picks Today
 [Exclusive] "Forecasts of Over 10 Billion, but Only 100 Million Earned"... 95% Followed This Pattern: Why Are KOSDAQ Special Exception IPOs Inflated? [KOSDAQ Inflated IPOs]①
- "Breakfast Now" Hits 1.41 Million Views... Burger King Expands Morning Menu Nationwide After 8x Sales Surge
- "My Debt Is 73 Million Won"... Sharing Every Repayment Led to an Unexpected Turn
- "Drinking This in the Morning Is Like Drinking Alcohol"..."Doctors Warn: Never Consume It"
- Is 'KOGUMA' Coming Too?... "Japan in Serious Trouble" - Archipelago on High Alert Ahead of Holidays
A financial sector official said, “Given that network separation has been relaxed, it is important to use AI proactively to identify and fix vulnerabilities. The regulatory authorities are also encouraging financial firms to step up their use of AI for security purposes in this context.”
© The Asia Business Daily. All rights reserved. Unauthorized AI training and use prohibited.