Claims of "Unbreakable Security" Shattered as Banks' Security Blind Spots Exposed
Spread of AI-powered Automated Attacks
Shinhan, KB Kookmin, and Hana
Customer Data Breach through Business Support Systems
Major banks have continually highlighted their top-tier information security systems. However, repeated hacking incidents exploiting system vulnerabilities have led to customer information being compromised. As automated attacks using artificial intelligence (AI) become more widespread, experts point out that there is a need for fundamental solutions to translate existing security frameworks into tangible information protection outcomes.

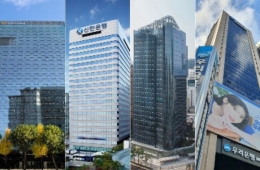
According to the semiannual reports of financial holding companies released on October 5, KB Kookmin Bank, Shinhan Bank, and Hana Bank have all underscored their specialized teams and capabilities for protecting customer data. In its most recent semiannual report, Shinhan Bank announced that it achieved an S grade (100 points) for the sixth consecutive year in the “Personal Credit Information Management and Protection Assessment” led by the Financial Services Commission. The bank also disclosed that it has secured both domestic and international security certifications such as ISMS/ISMS-P and ISO27001, and that it has dedicated internal teams for responding to cyberattacks and conducts regular security drills in coordination with the Financial Security Institute. Notably, Shinhan Bank emphasized that it was the first financial institution in Korea to participate in the NATO Cooperative Cyber Defence Centre of Excellence's “Locked Shields” exercise.
KB Kookmin Bank stated that it applies additional authentication procedures for accessing customer information and ensures that only authorized employees can access personal data. The bank explained that it continuously monitors the entire process from data collection to destruction and conducts on-site inspections of external contractors handling personal information.
Hana Bank also disclosed that its integrated security monitoring center is operated 24 hours a day, 365 days a year at its main data center, and that access to personal data is permitted only for business purposes, with usage purposes and reasons being registered and managed accordingly.
Nonetheless, actual incidents occurred in areas that had not been adequately guarded. Shinhan Bank’s loan broker inquiry service, KB Kookmin Bank’s internal mobile work support system for employees, and Hana Bank’s business support system all had vulnerabilities that were exposed to attacks.
The Financial Supervisory Service, during an emergency meeting of the financial sector convened the day before, raised concerns about the potential for large-scale automated attacks using AI agents. Major risk factors identified included systems where data could be browsed without personal authentication, lack of proper access controls, and cases where known vulnerabilities were not remediated in a timely manner.
The core problem is that, if automated AI-based scanning becomes more common, even minor systems that were previously not a management focus may become targets for attack. This means that existing security frameworks, which have mainly concentrated on preventing customer service outages and defending core networks, are now insufficient for managing every potential threat vector.
Yi Eogwon, Chairman of the Financial Services Commission, stressed the importance of this issue the previous day, stating, “A single unmanaged gap can become a vulnerability in the entire security framework,” and emphasized the need to establish a system where ‘AI attacks are defended by AI’.
Hot Picks Today
 "I Ate at Home to Save Money, But My Account Balance Was Still a Shock"
- Suddenly Called Out During Class, Awarded $100,000 as Students Cheer in the Gym
- "Bought It Cheaper in Japan Than Korea"... Improper Use Leads to Vomiting and Abdominal Pain, Official Warning Issued
- "After a Dream About Feces, Bought a Lottery Ticket and Won 20,000 Won... Scratched Again and Hit a 2 Billion Won Jackpot"
- "Uncle Will Buy Them All for Wonie"... Men in Their 30s Sweep Up 600,000 'RESCENE Bread'
The government is working to relax regulations around network separation and to establish joint detection and response frameworks within the financial sector. However, since even large banks have recently suffered incidents, smaller financial institutions that lack specialized personnel and sufficient budgets are likely to be even more vulnerable to these threats. A financial industry source commented, “We need to strengthen the responsibility for managing vulnerabilities at individual financial companies, while also expanding joint inspections and information sharing to help bridge the security gap between institutions.”
© The Asia Business Daily. All rights reserved. Unauthorized AI training and use prohibited.