"Hacker’s Identical IP Detected Across Financial Institutions... Large-Scale Attacks Using AI"
Amid a series of recent hacking attacks targeting the financial sector, it has been confirmed that the same hacker’s Internet Protocol (IP) address was detected across multiple banks.
According to financial authorities on the 4th, the same attacker’s IP address was discovered in the security breach incidents at seven companies: Shinhan Bank, KB Kookmin Bank, Hana Bank, BNK Busan Bank, Yegaram Savings Bank, Welcome Savings Bank, and Hyundai Capital. It was found that the attacker persistently changed their IP address while continuing the attacks.

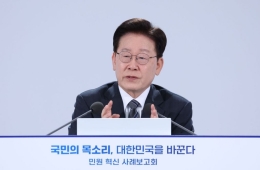
Lee Eokwon, Chairman of the Financial Services Commission, is speaking at the recent emergency inspection meeting for all financial sectors' response to infringement threats held on the 4th at the Government Complex Seoul. Photo by Yonhap News
View original imageNotably, it is believed that the attacker utilized AI tools to carry out large-scale automated attacks targeting multiple financial institutions simultaneously.
In fact, according to materials reported by Shinhan Bank to the National Assembly, the attacker in the Shinhan Bank hacking incident used IP addresses from several countries, including Korea, the United States, Japan, Hong Kong, Singapore, Vietnam, Thailand, and the United Kingdom.
Financial authorities classified the hacking incidents into three types and instructed firms to respond accordingly. In information inquiry services, it was discovered that the system had been developed to allow inquiries on loan applications and corporate representative information without user authentication. As a result, authorities called for a comprehensive review to identify and correct any services lacking proper verification procedures, or to suspend such services altogether.
For employee work-support services, data breaches occurred due to a lack of mobile device access control or unaddressed web vulnerabilities that allowed unauthorized access. Moving forward, access will be restricted to pre-registered devices, and vulnerable web services are to be improved. Regarding homepage services, it was found that hackers exploited already-known security vulnerabilities to install malicious code and steal log files containing customer information. Authorities instructed that identified vulnerabilities must be fixed or the affected services suspended, in order to strengthen security controls.
The financial authorities plan to conduct on-site inspections of companies affected by the incidents and, based on the inspection results, will share identified vulnerabilities and improvement cases to prevent the recurrence of similar incidents.
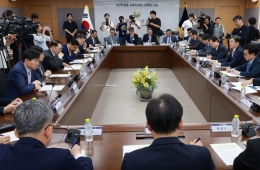
Meanwhile, financial authorities have held a total of three emergency situation response meetings since the hacking incidents occurred. At the meeting on this day, all financial sector heads and executives from financial institutions gathered to discuss response measures.
Hot Picks Today
 "Bought It Cheaper in Japan Than Korea"... Improper Use Leads to Vomiting and Abdominal Pain, Official Warning Issued
- "I Pay and Check Out Myself"…Self-Checkout Sparks Outrage, Leads to Proposed 10% Discount Bill
- "Boss, What Is This?" The 2,000 Won 'Pizza-Like Rice Cake' Causes a Sensation at Local Shops [Flavor File X]
- "In My Eyes, I'm Still 28"... Chinese Woman Gives Birth to Son at 58 and Daughter at 60
- "Uncle Will Buy Them All for Wonie"... Men in Their 30s Sweep Up 600,000 'RESCENE Bread'
Lee Eogwon, Chairman of the Financial Services Commission, urged, "The entire financial sector must recognize the seriousness of the current situation and exercise the highest level of vigilance," emphasizing rigorous security inspections and consumer protection efforts.
© The Asia Business Daily. All rights reserved. Unauthorized AI training and use prohibited.