Lee Eogwon Orders Comprehensive Inspection of Exposed IT Assets in Financial Sector Hacking Case: "Strict Action for Similar Incidents"
Emergency Inspection Meeting Held Across Financial Sector; Lee Chanjin and Others in Attendance
Comprehensive Review Ordered of External Interfaces, Authentication, and Access Controls
Principle of Blocking All Nonessential External Access A
Lee Eogwon, Chairman of the Financial Services Commission, ordered a comprehensive reassessment of information security systems across the entire financial sector after multiple financial institutions, including major commercial banks, recently experienced hacking attempts leveraging artificial intelligence (AI). He instructed that all externally exposed IT assets and services be thoroughly inspected, and that any external access not essential for operations be fundamentally blocked. The authorities also warned that, if appropriate measures are not taken despite previously shared attack information and incident cases, and similar incidents recur, strict action will be taken.

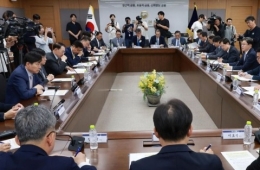
On October 4th, during an emergency inspection meeting for the entire financial sector, held at the Government Complex Seoul to address recent threats of breaches, Chairman Lee Eogwon made these announcements. The meeting was attended by Lee Chanjin, Governor of the Financial Supervisory Service; Park Sangwon, President of the Financial Security Institute; heads of industry associations; as well as CEOs of major commercial banks and other key financial institution representatives. The Ministry of Science and ICT, the Personal Information Protection Commission, and the National Police Agency also participated, agreeing to review the interagency response system and strengthen joint cooperation.
The financial authorities initiated this emergency inspection because signs of cyberattacks against major financial institutions have been identified repeatedly in recent days. Since receiving the breach report from Shinhan Bank on September 30, the authorities have launched an on-site investigation to determine the cause and extent of the incident. Investigations into breach reports from other financial firms are also ongoing.
Financial authorities have instructed the entire financial sector to thoroughly reassess all external interfaces and threat detection systems. They are required to comprehensively identify all IT assets and services exposed to external networks, check for security vulnerabilities, authentication and access controls, and examine intrusion detection capabilities. Not only banks and credit card companies, but also cooperatives, savings banks, insurance, securities, fintech firms, and other small and medium-sized financial institutions must complete self-inspections as quickly as possible and report the results to the Financial Services Commission and the Financial Supervisory Service.
They must also verify whether previously shared attacking IP addresses, attack methods, and breach attempt histories have been properly incorporated into each company’s detection and blocking systems. The authorities stated that, if inspection and response to these shared attack details are neglected and similar incidents occur, strict action will be taken in accordance with relevant laws and regulations.
Control over external access points will also be strengthened. Financial institutions are required to identify and check not only customer-facing services, but also all external access points and system access routes used by employees in the course of their work. Unless an external connection is absolutely essential for providing services or performing work, outside access must be fundamentally blocked. Even when unavoidable, access permissions and the information available for inquiry must be minimized.
In particular, systems used by external personnel such as loan brokers and outsourcing firms, as well as staff members—which have been identified as a cause of recent breaches—must be closely reviewed. Institutions must ensure that personal credit information is not stored or accessed unnecessarily, and must check whether there are access routes where authentication steps are missing or can be bypassed.
Measures to prevent consumer damage are also being strengthened. Any financial company that experiences a breach must quickly determine the scope of leaked information and the potential for consumer damage, and immediately implement measures to prevent further information leaks or financial losses. If damage is confirmed, the company must notify affected consumers and commence remediation and compensation procedures. In order to guard against secondary damages such as voice phishing or smishing, detection of abnormal financial transactions and consumer notifications will be further reinforced.
Additionally, the financial authorities plan to expand the sharing of threat information between financial companies and related institutions. Attack IPs, methods, and attempted breach details identified in recent incidents will be swiftly disseminated to enable immediate detection and blocking by other firms. Interagency cooperation will be bolstered, including with the Ministry of Science and ICT, the Personal Information Protection Commission, and the National Police Agency. Sharing of threat intelligence across other industries is also expected to expand.
The transition to AI-powered security systems is also set to accelerate. The authorities emphasized current measures to urgently relax and review network separation regulations, and directed the financial sector to adopt “AI-defends-against-AI-attacks” security systems based on artificial intelligence technology.
Hot Picks Today
 "They Look Just Like Chestnuts"...Carelessly Picking Them Up Could Be Dangerous: Avoid Eating These Street Fruits
- "Bought It Cheaper in Japan Than Korea"... Improper Use Leads to Vomiting and Abdominal Pain, Official Warning Issued
- "Boss, What Is This?" The 2,000 Won 'Pizza-Like Rice Cake' Causes a Sensation at Local Shops [Flavor File X]
- "In My Eyes, I'm Still 28"... Chinese Woman Gives Birth to Son at 58 and Daughter at 60
- "Uncle Will Buy Them All for Wonie"... Men in Their 30s Sweep Up 600,000 'RESCENE Bread'
Chairman Lee Eogwon stated, "Security vulnerabilities in a single financial institution are increasingly likely to become risks for the entire sector. The financial industry must treat this incident as a lesson to thoroughly reassess all information security systems from scratch, with an exceptional sense of vigilance and the highest level of alertness, and to enhance their security posture." He continued, "We will rapidly and clearly determine the substance behind these new threats through rigorous root-cause investigations, and meticulously supervise the thorough implementation of consumer protection measures." He also stressed the need to analyze the types and patterns of breaches and damages in order to pursue necessary institutional improvements.
© The Asia Business Daily. All rights reserved. Unauthorized AI training and use prohibited.