Evidence of “AI in Chinese” Detected... Widespread Hacking Attacks Hit Banking Sector (Comprehensive 2nd Report)
Traces of a Chinese-Language Console Found on Attack Server
"Actual Use Remains Unconfirmed"
Financial Services Commission Orders Emergency Bank and Card Company Inspections
Amid a series of hacking incidents involving financial firms such as Shinhan Bank and KB Kookmin Bank, evidence has emerged suggesting that attackers may have used artificial intelligence (AI)-based automation tools. Financial authorities have instructed banks and card companies to conduct internal security checks and have begun investigating the causes and techniques of the attacks.

According to the security industry on October 2, a string meaning “AI autonomous penetration testing console” in Chinese was discovered on the webpage of an attack server believed to be targeting Shinhan Bank. This is related to “ARTEX AI,” an open-source large language model (LLM)-based penetration testing system. However, it remains unconfirmed whether this tool was actually used in the hacking attempts.
ARTEX AI is a tool designed to automate information gathering, vulnerability scanning, and attack path planning. Although it was developed for security assessments, there are concerns that if abused by attackers, it could be used to automate and increase the efficiency of cyberattacks.
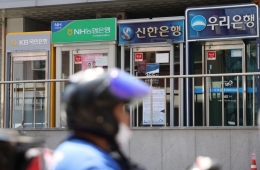
In the financial sector, there have recently been confirmed cases of information leakage or hacking attempts at Shinhan Bank, KB Kookmin Bank, Hana Bank, and BNK Busan Bank. At Shinhan Bank, an attack bypassed the identity verification process for a loan broker-exclusive service, resulting in a leak of information belonging to about 25,000 customers. At KB Kookmin Bank, an external breach of the employee mobile work support system led to the leakage of personal information for 119 customers.
On the same day, Hana Bank experienced unauthorized access through its business support system, resulting in the exposure of information for 89 customers. That day, BNK Busan Bank also detected the exposure of personal data for 11 outsourced developers. While there were also hacking attacks at Woori Bank and NH Nonghyup Bank, it is reported that no information leak occurred in those cases.
On this day, the Financial Services Commission held an emergency response meeting for the financial sector, presided over by Secretary General Shin Jin-chang, to share details of the recent data breaches, attack types, and methods. Secretary Shin directed banks and card companies to conduct thorough self-inspections of all externally exposed IT systems.
Financial institutions are required to inspect their externally exposed IT assets and services, security vulnerabilities, and access control status. The financial authorities plan to share IP addresses used in the attacks and records of intrusion attempts with relevant agencies, and will receive reports on the results of internal inspections swiftly.
The Financial Services Commission, Financial Supervisory Service, and Korea Financial Security Institute have sent on-site investigation teams to the four affected banks: Shinhan Bank, KB Kookmin Bank, Hana Bank, and BNK Busan Bank. The authorities plan to analyze the causes and techniques of the attacks and to establish plans for system improvements.
Hot Picks Today
 "A Seafood Feast and a Fraudulent Act: The Fate of a 20-Something American Who Tried to Dine and Dash $63"
Secretary Shin stated, "We will closely monitor attempted intrusions in the financial sector and engage in close cooperation by rapidly sharing threat intelligence. We will thoroughly analyze the causes and attack methods of these incidents and swiftly develop measures to improve the system."
© The Asia Business Daily. All rights reserved. Unauthorized AI training and use prohibited.