Institution Heads to Face Disciplinary Action for Information Leaks and Ransomware Incidents in the Public Sector
When public sector organizations experience cyber security breaches, disciplinary action will be further strengthened, especially focusing on high-level officials. This move follows criticism that, although most information leakage incidents were caused by failure to follow basic guidelines, appropriate disciplinary measures were not being taken against administrators. The government plans to raise the standards for disciplinary action regarding violations of basic security rules so that, going forward, the head of the relevant institution will be held primarily responsible.
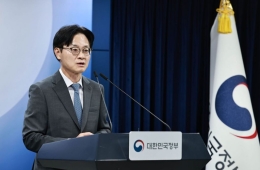
On October 1, the Ministry of the Interior and Safety announced these measures as part of its "Plan to Strengthen Cybersecurity Accountability in the Public Sector," in cooperation with the National Intelligence Service, the Ministry of Personnel Management, and the Personal Information Protection Commission.
According to the Ministry of the Interior and Safety, most recent public sector cyber security incidents—including the hacking of the Onnara system, ransomware infections at national university hospitals, and personal information leaks from the Korea National Diplomatic Academy and the Institute for Information & Communications Technology Planning & Evaluation—resulted from failures to comply with basic security rules. Despite this, institution heads who were not political appointees were excluded from disciplinary action. Between 2021 and May of this year, among approximately 247 cases of information leakage in the public sector, there were zero instances where the institution head was disciplined. Only 9 cases involved disciplinary measures against those in charge or managers, representing merely about 1% of the total. The Ministry of the Interior and Safety analyzed that, because the results of the "cybersecurity status evaluation," which assesses compliance with cybersecurity rules, contributed just 0.6 out of 100 points in the overall government work evaluation, there was insufficient incentive for organizations to improve their cybersecurity efforts.
Accordingly, when an information leakage incident occurs in the public sector, the government will increase the standards for disciplinary action for breaches of cyber security rules and will explicitly stipulate stronger accountability regulations for high-level supervisors. The Ministry of Personnel Management plans to introduce new provisions in the "Enforcement Rules for Civil Servant Discipline Decree" in November, establishing strict supervisory responsibility in the event of information leakage incidents. In addition, the National Intelligence Service will expand the scope of its "cybersecurity status evaluation" to all public sector institutions by 2028, increasing the number of organizations assessed from 153 to 2,160.
Measures will also be put in place to prevent a tendency to avoid work related to cyber security amid the tougher disciplinary actions for security breaches.
Hot Picks Today
 "From 20s to 60s, Everyone Rushed In"...The 'Top License' Also Obtained by Actors Yoo Yeon-seok and Sung Hoon Revealed
- "Unbelievable Event" in Tokyo Leaves Japan Stunned...Even 'Weather-Related Illnesses' Emerge
- Smoking Cigarettes and Taking Photos at Gyeongbokgung Palace..."I Don't Know How to Smoke," Foreign Tourists Deny Accusations
- SNU Students Line Up for This Recruitment Fair: "Better Than Large Corporations" [Report]
- "The Real Winner Controls the Heat"...LG Electronics Bets 150 Billion Won on New Chiller Plant in Virginia, US
New information security work allowances will be established, and those in charge of information security will be given preferential treatment through additional points in their performance evaluations. In terms of organization and budget, central administrative agencies and metropolitan governments will strengthen their cyber security workforce. In the mid to long term, dedicated organizations led by private-sector experts will be established to further enhance professional capabilities.
© The Asia Business Daily. All rights reserved. Unauthorized AI training and use prohibited.