"AI Means Intelligence, Web3 Means Trust"... Raonsecure Unveils Agentic AI Control Solution
Jensen Huang of NVIDIA: "Cybersecurity Is the Next Major Application for AI"
The Foundation of AI Safety Starts with Authentication
Web3-Based Identity, Authorization, and Accountability Management on the Rise

As artificial intelligence (AI) evolves from merely answering questions to making independent decisions and taking actions as "agentic AI," the focus of the AI industry is shifting from "performance" to "safety."
Recently, the global AI industry witnessed a rare scene. Dario Amodei, CEO of Anthropic, proposed the need to control the pace of AI advancement so that technical safety mechanisms and institutional management frameworks can keep pace. In response, rival executives such as Sam Altman, CEO of OpenAI, and Elon Musk also publicly expressed agreement. Amodei further suggested continuous verification of major AI companies’ systems by independent external evaluators.
Previously, Jacob Coxon, a researcher at Anthropic, warned upon leaving the company that accelerating competition in AI development could push safety measures to the background. As the possibility of "recursive self-improvement," where AI accelerates its own development, is raised, concerns are also mounting over a widening gap between AI advancement and the ability to control it.
Ultimately, the debate is shifting from whether to halt AI development to how much autonomy should be given to AI and how to ensure its safe control. Agentic AI is different from conventional generative AI. It not only answers questions, but also accesses enterprise systems, retrieves data, works across multiple applications, and independently executes tasks. The role of AI is shifting from merely answering queries to actually performing work.
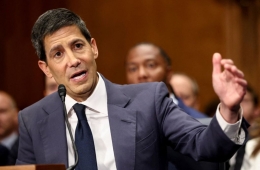
This change is also giving rise to a new security market. Recently, Jensen Huang, CEO of NVIDIA, identified cybersecurity as the next major application for AI at the Goldman Sachs Technology Conference. As AI further automates coding, both offensive attacks that seek out vulnerabilities and defensive responses to block them will increasingly become centered around AI, driving higher demand for AI in the field of cybersecurity.
As AI emerges as both attacker and defender, the scope of security is expanding. In the future, security will not just involve blocking external attacks; it will also require identifying and controlling "which AI is acting," "who authorized it," "what it is allowed to access," and "what actions it has taken."
Just as people require ID cards and access rights, AI agents now need verifiable digital identities and authorization frameworks. The key to the agentic AI era is not to eliminate autonomy but to implement "controlled autonomy," allowing just as much independence as needed while carefully managing its boundaries.
At this point, the industry is paying close attention to the technology portfolio of Raonsecure. Raonsecure plans to unveil five agentic AI security solutions at the "SecuUp Seminar" later this month, covering everything from technologies that manage AI agents’ identities and permissions and control risky behaviors, to detecting and responding to security threats using AI.
Another core element is blockchain-based Decentralized Identity (DID). As AI agents perform tasks or interact with other systems on behalf of humans, a framework to verify "which AI it is" and "which authorities have been delegated" becomes crucial. Raonsecure has accumulated digital identity technology and reference experience by building national mobile ID schemes such as mobile driver’s licenses, mobile government employee cards, and national veterans’ registration cards.
Expanding this to the AI field, it becomes possible to assign verifiable identities to AI agents and confirm to whom and what permissions have been delegated.
Raonsecure’s distinguishing factor is not simply owning both AI security and digital identity technologies, but its ability to connect them into a streamlined process of identification, authorization, action control, and accountability tracking.
DID proves "which AI is acting," authorization management establishes "what it can do," and agentic AI security controls what the AI is actually doing. Throughout this process, Web3 technologies—including blockchain and DID—can serve as trust infrastructure for verifying AI identities, delegated permissions, and execution histories.
As AI performs more tasks and is granted greater authority, the standard for competition is likely to shift from "how smart the AI is" to "how trustworthy and reliable it is for assigned work." The importance of "trust infrastructure" that identifies, authorizes, and controls AI agents’ actions will only grow.
Hot Picks Today
 "Even Hard-Earned Money Can't Buy It"…Hanwoo Beef Sales Drop Sharply After Three Years
- "Even a 45 Million Won Bonus Isn't Enough"...Why Did the Micron Union Reject a Record-Breaking Performance Bonus?
- "Up to 5 Million Won a Month, No Retirement Age: What Is the 'Second Career' Exploding in Popularity Among the 50s and 60s After Retirement?"
- 'Pronounced Dead,' Now Boiling Again... Chinese Millennials and Gen Z Seek 'Premium Ramen'
- "The Clothes My Dad Used to Wear"... Ralph Lauren, Beanpole, and Hazzys See Sales Surge as MZ Generation Embraces the Trend
This is why Raonsecure, possessing both agentic AI security and Web3-based digital identity technology, is aiming to position itself in the ‘digital trust infrastructure’ market as a new axis of growth in the AI era.
© The Asia Business Daily. All rights reserved. Unauthorized AI training and use prohibited.