Supreme Court: "No Corporate Liability for Personal Data Leaks If No Emotional Distress Proven" [Choi Seokjin's Law & Biz]
Criteria for Interpreting “Statutory Damages” Established under the Law
Seven Standards Set for Determining Emotional Harm
First Trials Underway in Coupang, DUO, and TVING Cases
The most notable ruling regarding the scope of corporate responsibility and compensation in personal data breach incidents is Supreme Court Decision 2023Da311184, which was delivered in December of last year.
In this ruling, the Supreme Court established the principle regarding the statutory damages system under the Personal Information Protection Act, stating that "a company can be exempted from liability for damages if it proves that no mental distress worthy of compensation as damages has occurred to the data subject," even if the victim does not specifically prove the actual amount of damages suffered.

The incident originated from a data breach in September 2021, when hackers attacked and leaked the personal information—including email addresses and passwords—of 403,298 members from "HappyCampus," an online knowledge marketplace platform that mediates transactions involving reports, theses, personal statements, test materials, and more. One of the victims, Ms. Yoo, filed a lawsuit against the platform operator, AgentSoft, seeking statutory damages (consolation money) of 300,000 won and delay interest under the Personal Information Protection Act.
In this case, both the courts of first and second instance acknowledged the company's negligence for failing to properly detect and block hacking attempts, such as by disabling the web firewall. However, they dismissed Ms. Yoo's claims, based on the following reasons: ▲ prior encryption measures had been taken for passwords; ▲ it was difficult to conclude that the mere leak of email addresses exposed data subjects to concrete and foreseeable risks; ▲ there was no evidence that the hacked personal information had been transferred to third parties or disseminated to the public or third parties; ▲ immediately after the incident, the defendant company reported the data breach to the Personal Information Protection Commission and the cyber investigation bureau, identified the cause of the breach and blocked the illegal access channel, sent a hacking notification letter to the plaintiff to inform her of the breach, and requested that she change her password.
While upholding the conclusion of the lower courts, the Supreme Court clarified the standard for interpreting statutory damage provisions under the Personal Information Protection Act, stating that “if there are special circumstances where Supreme Court precedents regarding the interpretation of statutes applicable to small claims cases are not clear and numerous cases to which these statutes apply are pending in the lower courts, the Supreme Court may rule on the interpretation and application of substantive law for the purpose of unifying statutory interpretation, even if the requirements for appeal in small claims cases are not met.”
At the time, the Supreme Court explained that, unlike Article 39(1) (Liability for Damages) of the Act, Article 39-2(1) (Claim for Statutory Damages) excludes "damages" suffered by the data subject as a requirement for a claim, stating, “In a modern society where the extensive processing of personal data is normalized, the legislative intent is to allow victims to easily seek remedies by ensuring they can receive a legally fixed amount of compensation from data handlers, even if it is difficult to prove damages, when there is a violation such as a data breach.”
However, the Supreme Court ruled, “This does not mean the obligation to compensate should be recognized even in cases where it is evident that no damage has occurred. Therefore, a data handler can avoid liability for statutory damages by arguing and proving that no mental distress worthy of compensation as damages has occurred to the data subject.”
Furthermore, the Court presented seven criteria to determine whether mental distress worthy of compensation as damages has occurred to the data subject: ▲ the type and nature of the leaked personal information; ▲ whether the data breach created an identifiable risk to the data subject; ▲ whether any third party has accessed the leaked personal information or the possibility of future access; ▲ the extent of the dissemination of the leaked personal information; ▲ whether there is the possibility of further legal interests being infringed due to the data breach; ▲ the data handler's management of the personal information and the circumstances leading to the breach; ▲ the measures taken to prevent the occurrence and further spread of damage as a result of the breach.
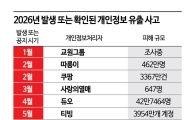
Meanwhile, in the SK Telecom hacking case, in which USIM information and more for approximately 23.24 million subscribers was leaked, three joint lawsuits—each claiming 500,000 won per victim—were consolidated, and the first hearing was held in March of this year. During the trial, the main issue was whether the 15,900 plaintiffs could be individually identified, focusing on the legal validity of "online powers of attorney."
Regarding the Coupang data breach incident, where personal information of approximately 33.67 million individuals was leaked, several complaints have been filed with the court since the first complaint was lodged in December of last year, and the first-instance trial is ongoing. In the case of Duo, a matchmaking company, which leaked the personal information—including resident registration numbers and marital history—of about 430,000 individuals, 46 victims filed a joint lawsuit in May of this year, each seeking 1 million won in damages.
Related Articles
 "Companies Handling Personal Data Should Have Incident Response Manuals and Conduct Drills" [Choi Seokjin's Law & Biz]
As for the TVING hacking incident, several law firms—including Law Firm Jihyang, which has already filed complaints on behalf of 140,000 victims—are proceeding with joint litigation, and in the GangnamUnni case, Law Firm YK is currently recruiting plaintiffs for collective actions.
© The Asia Business Daily. All rights reserved. Unauthorized AI training and use prohibited.