Personal Data Stolen for Blacklist... Samsung Union Chairman Referred to Prosecutors
Personal Information of Over 100,000 Compiled into Separate List
Union Membership Status Used to Create and Manage a "Blacklist"
Four Employees Who Illegally Accessed Personal Data Also Referred to Prosecutors
The chairman of the Samsung Group Union, which is a super-corporate labor union, as well as employees of Samsung Electronics who accessed the company's internal network without authorization, have been referred to the prosecution for creating a blacklist from the stolen personal information of 100,000 Samsung Electronics executives and employees.

Choi Seungho, Chairman of the Samsung Group Union and Samsung Electronics Branch. Photo by Yonhap News
View original imageOn September 4, the Hwaseong Dongtan Police Station in Gyeonggi Province announced that Choi Seungho, chairman of the Samsung Electronics branch of the Samsung Group Union, along with union executive A, had been referred to prosecution without detention on suspicion of violating the Personal Information Protection Act. Separately, four other Samsung Electronics employees, including employee B, who accessed the internal system abnormally, were also referred to the prosecution without detention for allegedly violating the Personal Information Protection Act.
According to police, around March of this year, when the approval of the union's industrial action led to an actual general strike, Choi and others allegedly used other employees’ personal information to compile a list indicating whether or not they had joined the union.
The police investigation revealed that A, who was responsible for work related to the company’s internal systems, unlawfully obtained a file containing more than 100,000 names of executives and employees and provided it to the union. Previously, in April, Samsung Electronics announced through an internal notice that "a list containing names of departments, names, employee numbers, and union membership status of dozens of people was delivered in a group messenger chat of a specific department." After filing a police complaint against an unidentified suspect, the company later identified A, who had collected personal data in bulk from the internal system, and filed an additional complaint specifically naming him.
The police conducted three searches and seizures at the Samsung Electronics headquarters and other locations, carrying out investigations based on the secured evidence. Several circumstances suggesting Choi’s involvement in creating a blacklist were also investigated, including a remark on YouTube in which he said, "We will manage as a list those who do not participate in the strike and work for the company."
B and three others are suspected of abnormally accessing the internal system with other employees’ personal information to check union membership status. Although the investigation found sufficient evidence of illegal access, their actions were limited to merely viewing the information, and they did not create a list or distribute it externally. These individuals were also confirmed to be members of the super-corporate union.
A police official stated, "The cases involving large-scale collection of personal information through the internal system by Choi and others, and the abnormal information queries by B and others, have been referred to prosecution as separate cases."
Meanwhile, Donghaeng Union, which is primarily composed of members from the DX (Device eXperience) division, released a statement the same day, saying, "If a list of 100,000 people was created, many of them would be our members," and criticized, "If a list revealing which union each person belongs to was compiled, it would itself constitute an infringement on members' right to union solidarity." The union also sent an official letter to the super-corporate union, demanding a response regarding the size, organizational scope, and specifics of personal data collected for those included in the list.
Hot Picks Today
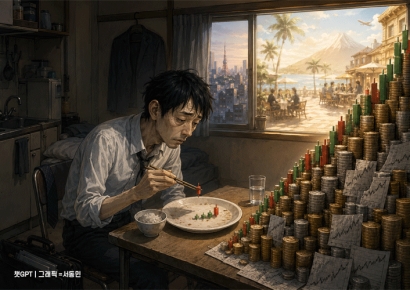 "Surviving on One Meal a Day to Invest 3.5 Million Won Monthly... 'FIRE' Craze Sparks 'NISA Poverty' in Japan"
- "Correction Over for Samsung and SK hynix" "670,000 for Samsung, 4.7 Million for SK hynix": Why Global IBs Remain Optimistic
- "As Soon as Yong Hyein Was Nominated... After a 195% Surge, This Stock Suddenly Plunged"
- "Used for the Wedding" 300,000-Won Ring and Dress...Changing Wedding Trends
- Causing Trouble Without a Simple "Sorry"... The Reason Behind the 'Gen Z Stare' Revealed
The union also urged Samsung Electronics, saying, "The company is both the complainant and the party responsible for management in this incident. The company must clarify by what route the personal data was leaked, and disclose what gaps existed in access rights and monitoring systems."
© The Asia Business Daily. All rights reserved. Unauthorized AI training and use prohibited.